Unit 4.case
Case Study: PCI & Gateway Integration for Nepali Merchants
Learning Objectives
By the end of this case study, you will be able to analyze a real-world payment integration strategy.
- ✅ Explain how Hosted Payment Pages (HPP) reduce PCI DSS scope for merchants.
- ✅ Describe the role of tokenization in enabling "saved card" features securely.
- ✅ Evaluate the function of 3-D Secure in mitigating fraud and payment disputes.
- ✅ Connect these technical choices to business outcomes like conversion rates and operational efficiency.
The Challenge: Moving Beyond Local Payments
Composite/illustrative case: no named retailer evaluation or measured outcome source was supplied.
A Nepali online retailer needed to expand its payment options beyond the standard methods.
Current State
- Cash on Delivery (COD)
- Local Wallets (e.g., eSewa, Khalti)
- Limitation: Low balance caps on wallets hindered high-ticket sales.
The Goal 🎯
- Accept international/domestic credit & debit cards.
- Increase conversion for expensive items.
- CRITICAL: Avoid the complexity and risk of handling card data directly.
Online Checkout

The Security Hurdle: PCI DSS
Payment Card Industry Data Security Standard (PCI DSS): A set of security standards designed to ensure that all companies that accept, process, store or transmit credit card information maintain a secure environment.
Directly handling card data is complex, expensive, and high-risk.
💡 The primary goal for any small-to-medium merchant is to reduce their PCI scope as much as possible.
Solution Part 1: The Hosted Payment Page (HPP)
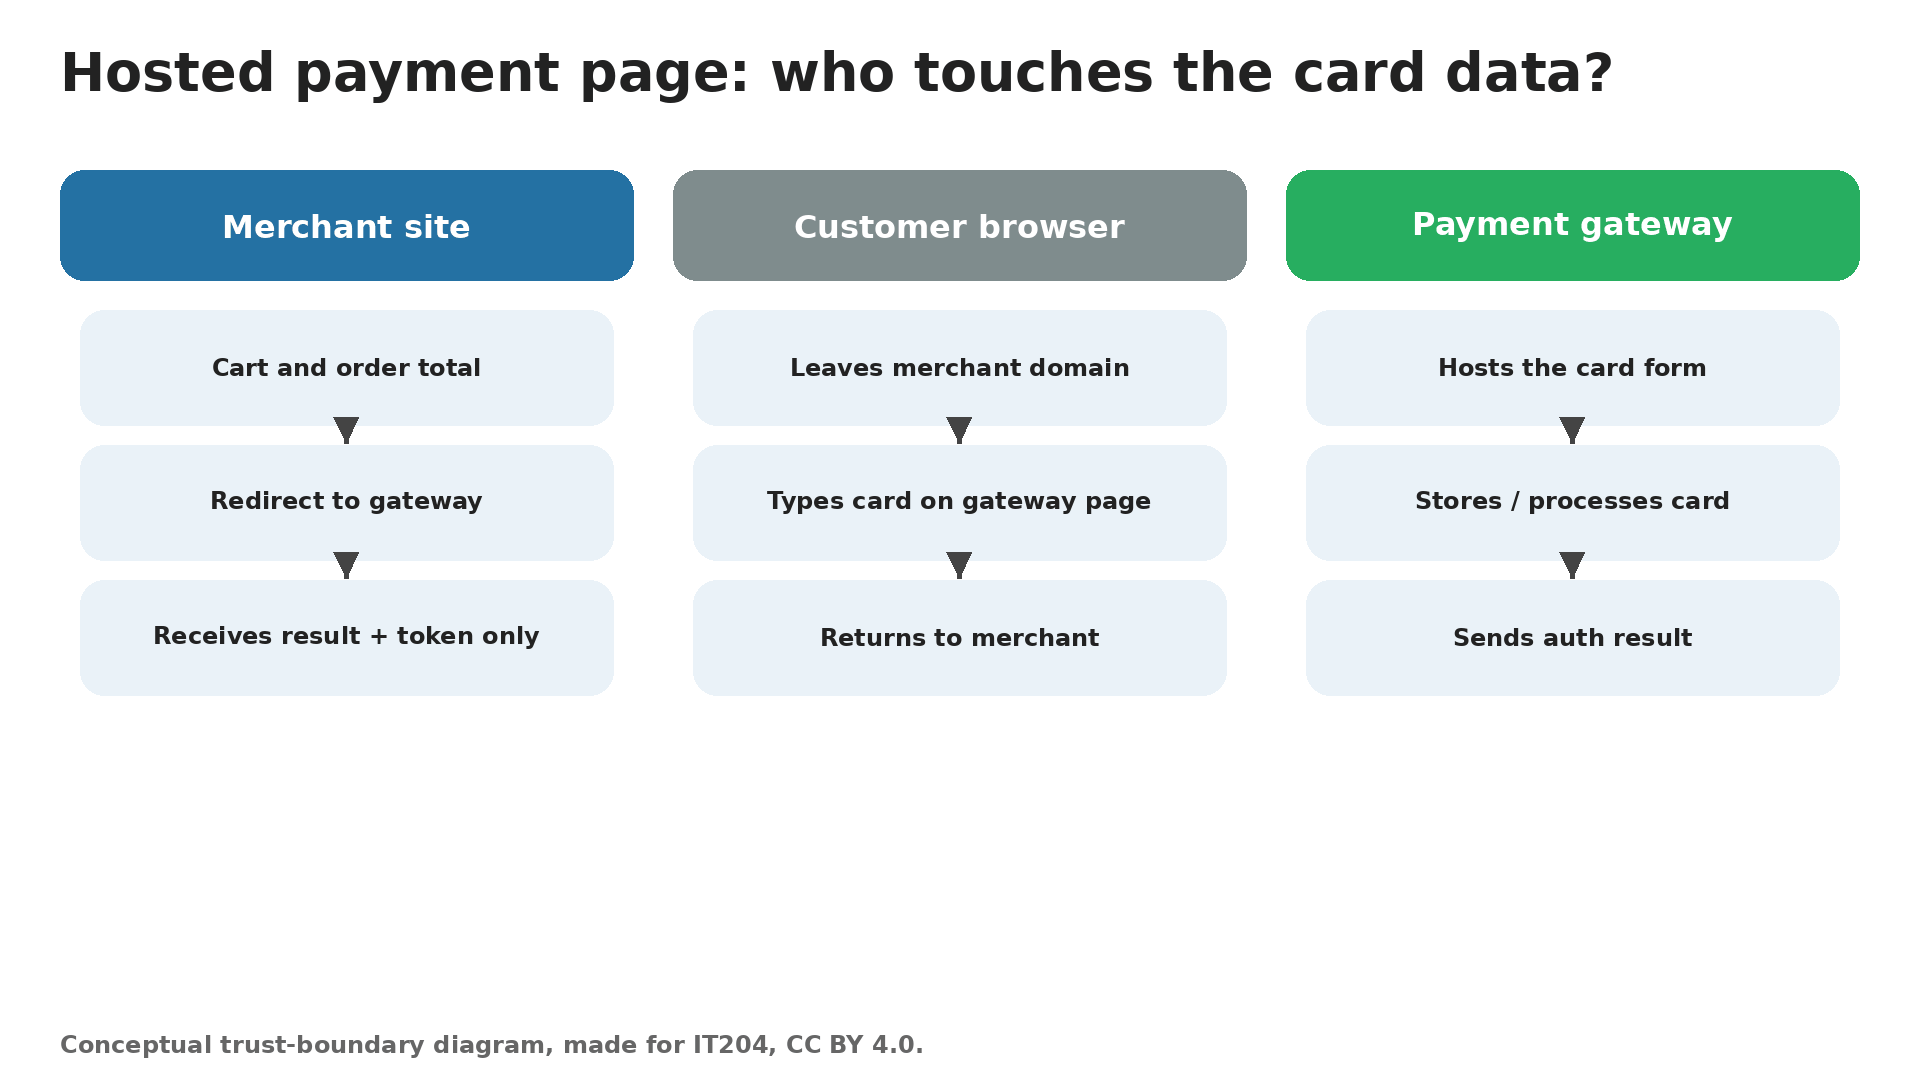
The merchant chose an integration method that keeps card data completely off their servers.
User Checkout Flow 🛒
- User clicks "Pay with Card" on the merchant's site.
- Browser is redirected to a secure page hosted by the Payment Gateway.
- User enters card details directly onto the gateway's page.
- Gateway processes the payment and redirects the user back to the merchant's site with a success/failure status.
Result: The merchant's system never sees or touches the raw card number. ⚡
Interactive: HPP Checkout Flow Simulator
Illustrative integration; named-provider availability and certification are unverified. HPP reduces scope, not every merchant responsibility.
Step through the Hosted Payment Page flow to see exactly where the customer's browser and card data are at each stage.
🎬 Watch: Whose Page Takes the Card?
Hosted Checkout Boundaries
The Customer Returns—but Is the Order Paid?
Scenario: the browser returns to /order-success, but the server has not confirmed payment. Should the warehouse ship?
- Treat the browser return as a user-experience signal, not final payment evidence.
- Verify a signed provider notification or retrieve payment status through the provider's authenticated server API.
- Match the merchant order ID, expected amount, currency and final payment state.
- Handle duplicate notifications idempotently: one payment event must not ship two parcels.
If status is uncertain, show “Payment being checked—please do not pay again yet.” Reconcile before fulfilment.
Reducing PCI Scope: SAQ A vs. SAQ D
This HPP approach drastically simplifies PCI compliance.
SAQ A (The Goal)
For merchants that completely outsource all cardholder data functions.
- Simplest questionnaire
- Fewest controls to validate
- Achieved via HPP / Redirect
SAQ D (The Nightmare)
For merchants who store, process, or transmit cardholder data.
- Most complex, lengthy questionnaire
- Hundreds of security controls
- Requires significant IT/security overhead
Choosing an HPP allows a merchant to qualify for SAQ A, the lightest level of PCI validation.
Interactive: Which SAQ Level Are You?
Simplified teaching model, not a PCI eligibility decision; see the following qualification slide.
Answer these 3 questions to determine your merchant's PCI DSS Self-Assessment Questionnaire tier.
Q1: Does your website directly collect card numbers (e.g., via a self-hosted input form or iFrame)?
Q2: Does your server store, process, or transmit any full cardholder data (PAN, CVV, expiry)?
Q3: Do you accept card payments through physical POS hardware at a brick-and-mortar store?
SAQ Types Are Not Merchant Levels
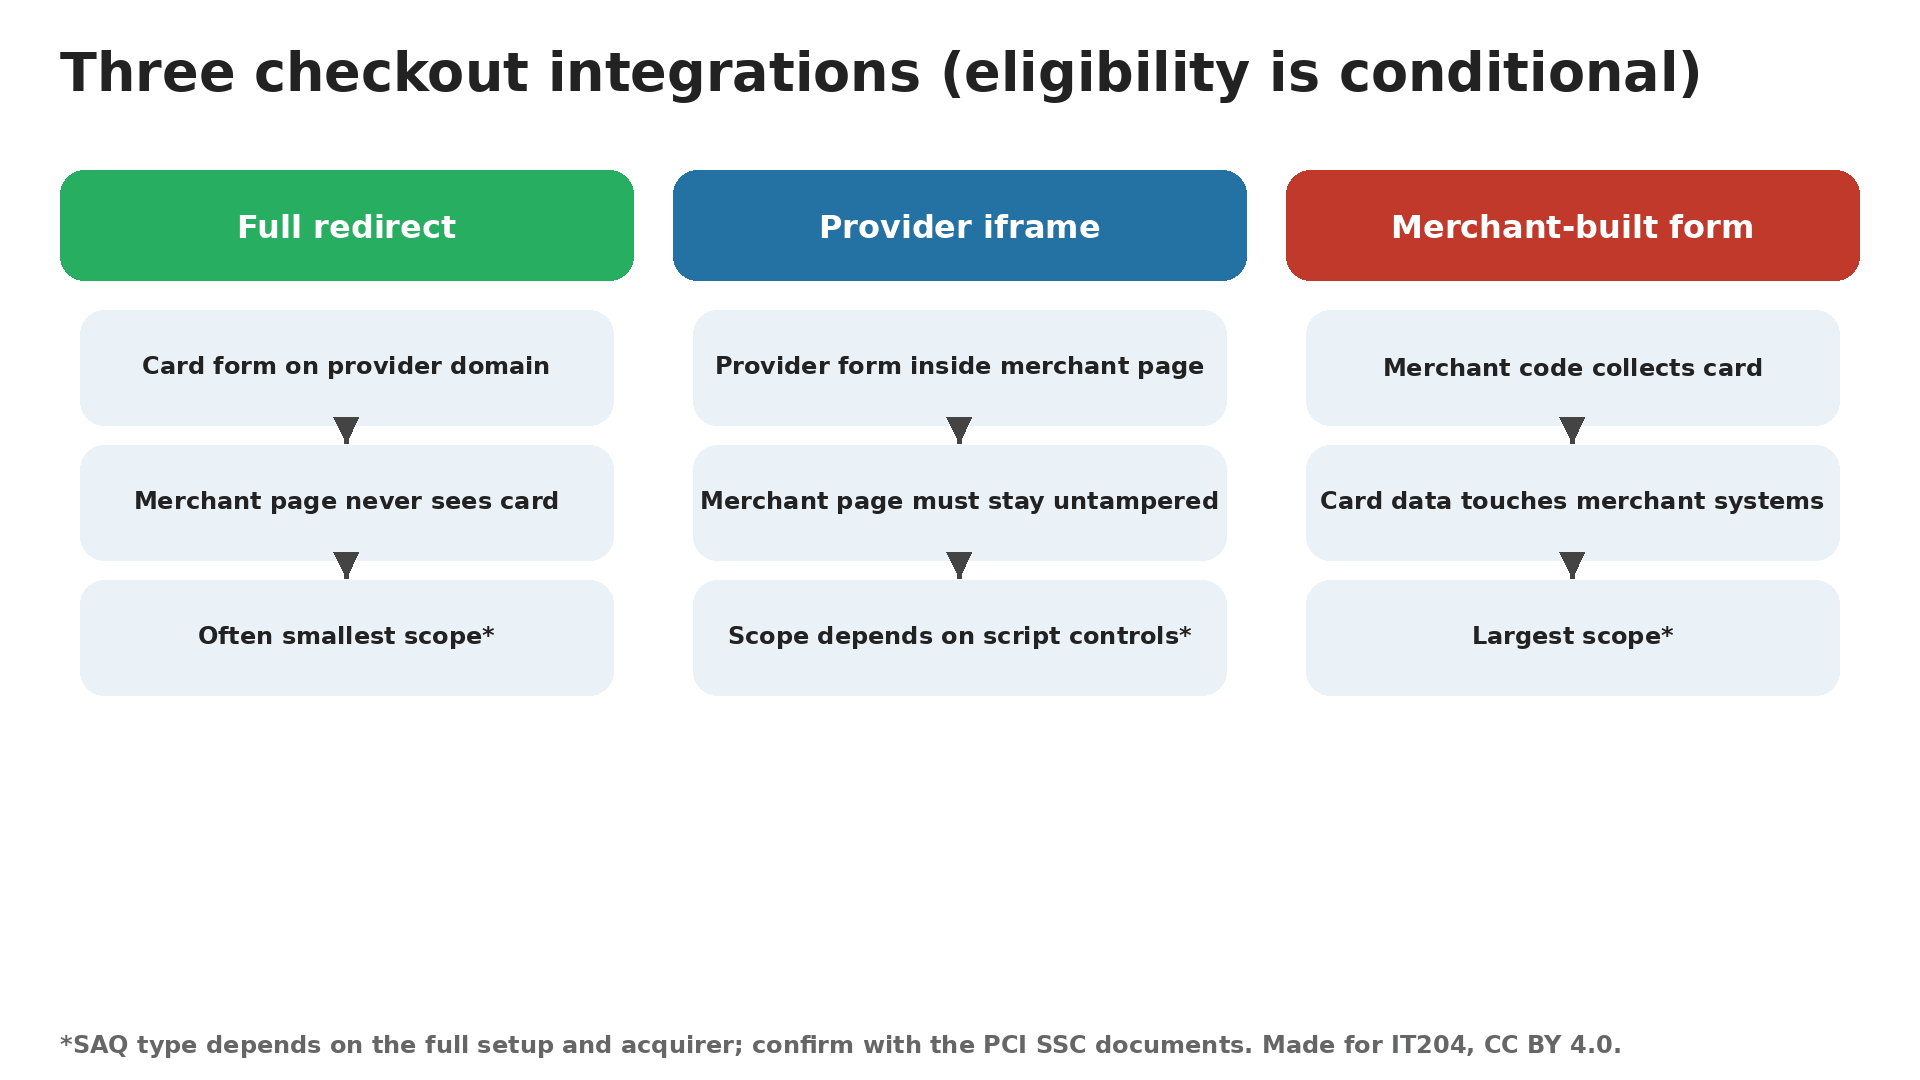
- SAQ type: selected from the actual payment architecture and all eligibility criteria. Merchant validation levels are a separate card-brand/acquirer concept.
- Redirect/HPP: can support SAQ A eligibility; outsourcing does not remove all merchant responsibilities.
- Provider-hosted iframe: is not automatically SAQ A-EP. The origin of payment-page elements and the full implementation matter.
- Merchant-generated form: can change scope even when card data posts directly to a provider rather than the merchant's server.
Confirm the current questionnaire and evidence with the acquirer/compliance-accepting entity. A three-question classroom quiz cannot certify eligibility.
Compare Checkout Integrations
Solution Part 2: Tokenization for Repeat Customers
How can the site offer a "save card" feature without storing card data?
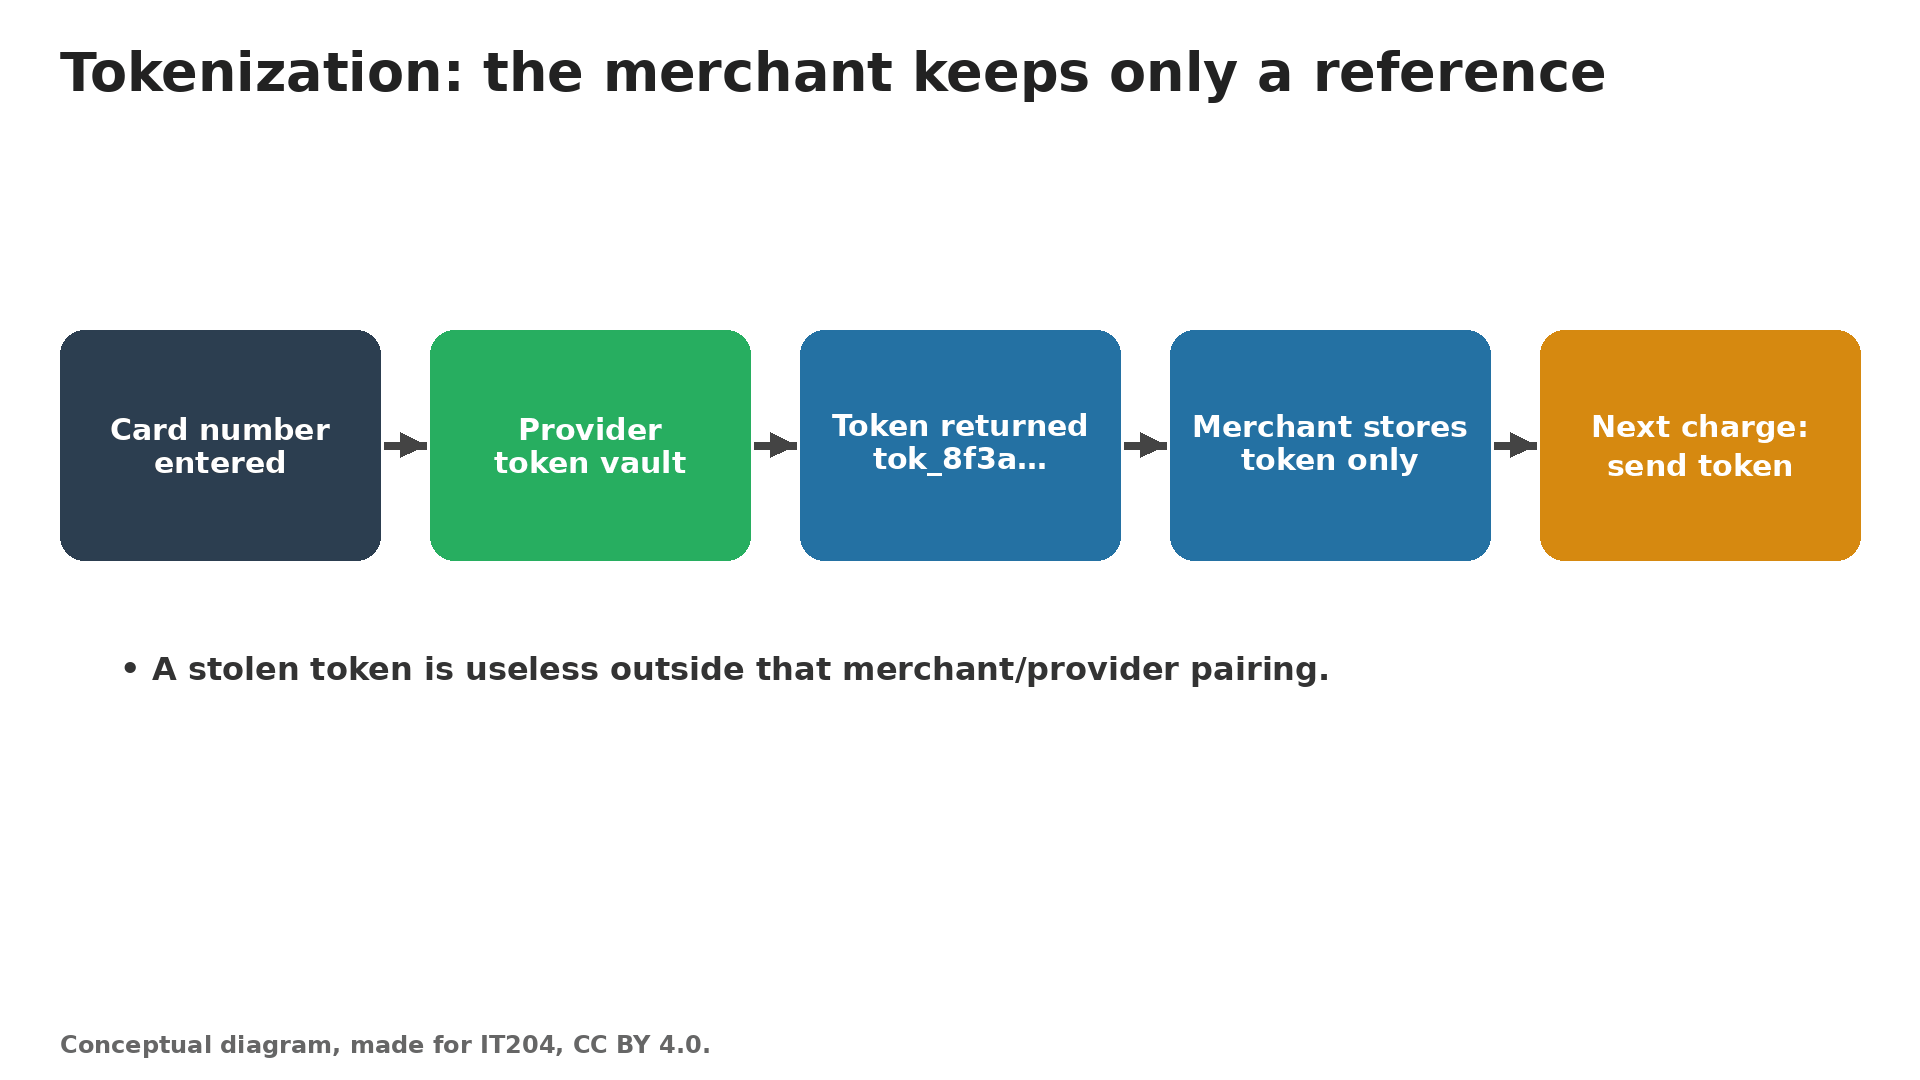
Tokenization: A process where sensitive card numbers are replaced with a unique, non-sensitive equivalent known as a "token." This token is useless to attackers.
🔍 How it Works:
- On first payment, the gateway saves the card details in its secure, PCI-compliant vault.
- The gateway returns a safe token (e.g., `tok_1Jabc...`) to the merchant.
- The merchant stores this token against the user's profile.
- For future payments, the merchant sends the token instead of the card details.
Interactive: Tokenization in Action
Use fake/test values only; never enter real card data. Browser token generation is an analogy, not a production vault.
Enter a fake card number and see how the gateway replaces it with a safe, meaningless token that the merchant stores instead.
A Token Reduces Exposure, Not Responsibility
- A payment token references protected card information; the merchant need not store the full card number to support repeat payments.
- A random token generated in this browser demo is a visual analogy—not a real vault, encryption scheme or production payment credential.
- An attacker with a usable token plus compromised merchant credentials may still abuse permitted payment operations. Protect access, API keys and customer accounts.
- Ask who can use the token, where it is accepted, how it can be revoked and whether future payments need customer authentication.
Use fake/test data only in class. Never store card verification codes after authorisation; tokenisation is not permission to retain CVV.
Keep Card Data in the Vault
Solution Part 3: 3-D Secure (3DS)
To prevent fraudulent transactions and chargebacks, 3-D Secure was integrated.
Frictionless Flow ✅
The customer's bank recognizes the transaction as low-risk and approves it instantly without any extra steps. This is the ideal user experience.
Challenge Flow 🔐
The bank requires an extra step for verification (Strong Customer Authentication - SCA). The user is prompted to enter:
- An OTP sent to their phone
- A password
- A biometric confirmation via their banking app
Benefit: Liability for fraudulent chargebacks often shifts from the merchant to the card-issuing bank.
Interactive: 3-D Secure Risk Assessment
Illustrative weights and thresholds, not an issuer algorithm. Authentication does not guarantee authorisation or eliminate all liability.
Adjust the transaction risk factors to see whether the bank's algorithm would trigger a Frictionless or Challenge flow.
What 3DS Does—and Does Not—Promise
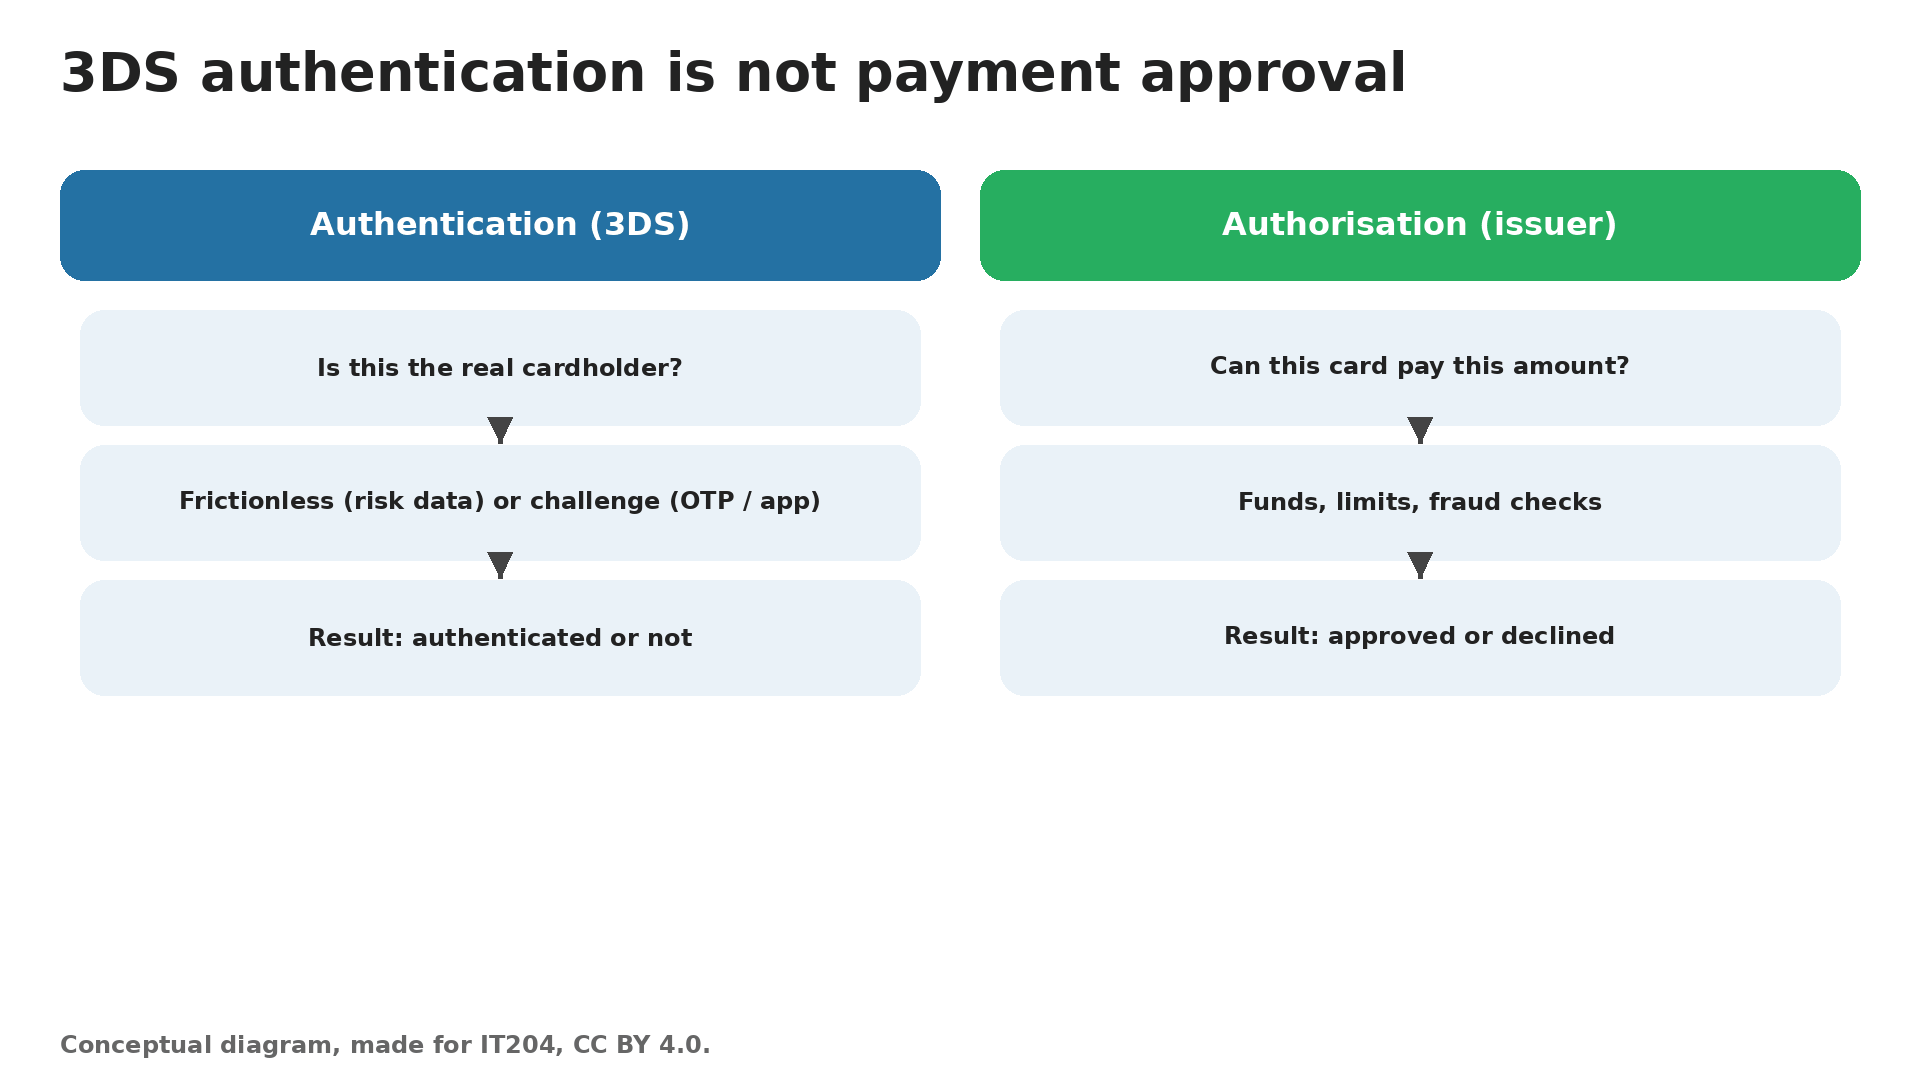
- Authentication: 3DS helps the issuer assess the shopper's identity through a frictionless or challenged flow.
- Authorisation: a distinct payment decision; the issuer may still decline an authenticated transaction.
- Liability shift: depends on scheme rules, eligibility and authentication results. It does not remove every dispute category, including non-delivery disputes.
- SCA: a regulatory concept in relevant jurisdictions, not a synonym for every OTP challenge or a blanket Nepal requirement.
The simulator's weights, thresholds and “soft/hard” labels are illustrative. They do not disclose any bank's real fraud algorithm.
🎬 Watch: Silent Pass or Challenge
Authentication vs Authorisation
Operational Impact: Automated Reconciliation 📊
Accepting a new payment type adds operational complexity. Automation is key.
Reconciliation: The process of matching transactions processed by the payment gateway to the funds deposited into the merchant's bank account.
- The payment gateway provides a daily settlement file (CSV, XML, or via API).
- This file lists all successful transactions and fees for that day.
- An automated script was developed to ingest this file and match it against orders in the internal accounting system.
- This eliminates hours of manual work and reduces human error.
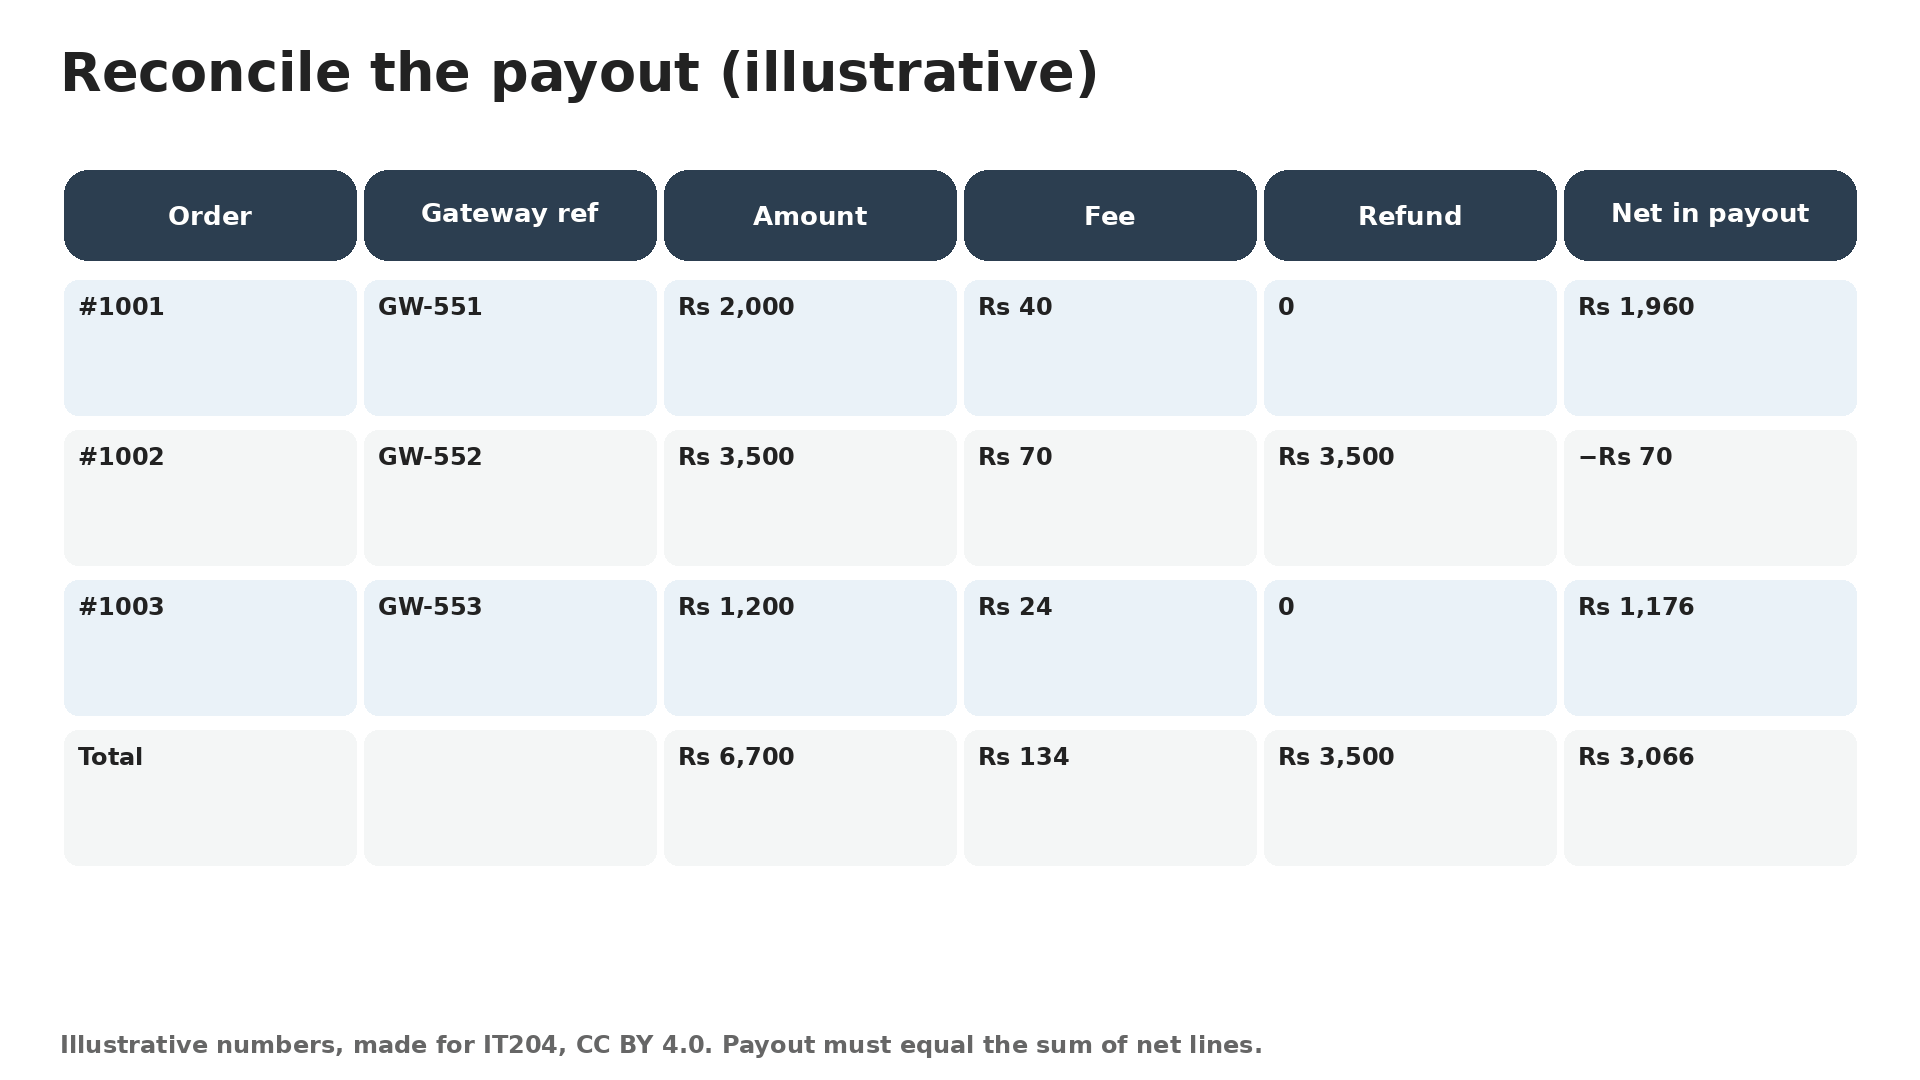
Worked Example: Reconcile the Payout
Illustrative daily batch: A captured Rs 3,000; B captured Rs 5,000; C declined Rs 2,000. Refund Rs 1,000 from A; fee 2% of captured value. No other adjustments.
- How much was captured? 3,000 + 5,000 = Rs 8,000; C is excluded.
- What is the fee under this assumption? 2% × 8,000 = Rs 160.
- Expected payout? 8,000 − 1,000 − 160 = Rs 6,840.
- If the bank shows Rs 6,740, what next? Investigate the Rs 100 difference using payout IDs, fee records and timing; do not invent a balancing transaction.
Real contracts may handle fees on refunds, reserves and settlement dates differently. Match by transaction and payout reference, not amount alone.
Illustrative Payout Ledger
Practical Application: The Nepali Context
Original provider ownership, local-partner and Nepal availability examples below remain unverified; do not treat them as onboarding advice.
This HPP and Tokenization model is a standard for enabling card payments in Nepal.
Local Gateways
Companies like NCHL (N-PAY) and local banks provide the infrastructure for card processing.
International Gateways
Merchants targeting tourists or international customers often use Stripe or Cybersource via a local partner bank.
Why it Works Here
It allows Nepali SMEs to access global payment standards without massive upfront investment in security infrastructure.
Case Outcomes & Business Impact
Composite/illustrative case: no named retailer evaluation or measured outcome source was supplied.
✅ Security & Compliance
- Card acceptance achieved with minimal PCI scope (SAQ A).
- Reduced fraudulent disputes and chargebacks due to 3-D Secure.
📈 Sales & Conversion
- Improved conversion rate for high-ticket items.
- Removed the "wallet balance" as a checkout blocker.
- Enhanced user experience with a secure, trusted checkout flow.
A smart technical strategy directly led to improved security posture and increased revenue.
Interactive: Business Impact Calculator
Illustrative gross model, not net profit: new costs are omitted; 75% liability avoidance and 8% sales uplift are assumptions, not guarantees.
Estimate the monthly financial benefits of implementing HPP + Tokenization + 3-D Secure for a Nepali online store.
Audit the Business Case Before Buying
Illustrative calculator defaults: 200 transactions × Rs 3,500 = Rs 700,000 revenue. The model assumes 2.5% chargebacks, 75% liability avoided and 8% extra sales.
- Model output: Rs 13,125 assumed avoided liability + Rs 56,000 extra revenue = Rs 69,125.
- That is not net profit: extra revenue must cover goods and fulfilment; integration, provider and authentication costs are omitted.
- If extra sales have a 25% contribution margin, they contribute Rs 14,000. Adding assumed avoided loss gives Rs 27,125 before new costs.
- Ask for measured baseline data and a pilot. The 75% and 8% assumptions are not published guarantees from a gateway or card network.
Key Takeaways
What are the core lessons from this implementation?
- 🎯 Prioritize PCI Scope Reduction: Always choose the integration method with the lightest possible compliance footprint. An HPP is often the best choice for non-enterprise merchants.
- 🔐 Never Handle Raw Card Data: Let the payment gateway's secure vault and tokenization system manage sensitive data.
- UX is Security: A clear, well-designed 3-D Secure flow and robust error handling are crucial for minimizing checkout abandonment.
- ⚙️ Think Beyond the Button: Plan for back-office operations like reconciliation from day one to ensure scalability.
Case Practice 📝
- What is PCI DSS, and why does using a hosted payment page reduce the retailer's PCI scope?
- Explain tokenization. How does it protect customers if the retailer's website is hacked?
- What is 3-D Secure, and which security dimensions does it support?
- Using the figures, explain the business case for adding card payments.
- What should the checkout show customers when a card payment fails, to avoid abandonment?
Revise the answers in the full note.
Sources & Media Credits
- Woman with card at laptop: Shixart1985, CC BY 2.0 (Wikimedia Commons).
- HPP, integrations, token-vault, authentication and reconciliation diagrams: made for IT204, CC BY 4.0.
- Videos: Cashfree Payments; Schellman.
- Image 1: source — CC BY 2.0, Shixart1985
- Clip 1: source
- Clip 2: source
- PCI SSC: SAQ eligibility
- Stripe: 3DS
- Stripe: payment lifecycle
Thank You
This case study demonstrates how strategic technology choices in payment systems can unlock growth while minimizing risk.
Next Up: Unit 4.6 - Digital Wallets and Mobile Payment Systems