Unit 9 · Session 1
Computer Security and Unauthorized Access
Today's focus
- Computer Security, Ethics, and Privacy
- Unauthorized Access and Protection
🎯 Learning Objectives
By the end of this session, you will be able to:
- ✅ Define the core concepts of computer security, ethics, and privacy.
- ✅ Identify major threats to digital information and key controls such as firewalls and encryption.
- ✅ Recognize the importance of cyber law and copyright in the IT profession.
- ✅ Define unauthorized access and describe the three main types of authentication factors.
- ✅ Explain the importance of strong passwords and two-factor authentication (2FA).
Computer Security, Ethics, and Privacy
The Core Concepts: A Digital Triad
This unit revolves around three interconnected pillars that are critical in today's digital world.
🔒 Security
Protecting information and systems from unauthorized access, use, disclosure, disruption, or destruction.
⚖️ Ethics
The moral principles that govern the use of computers and information systems. It's about what is right versus wrong in our digital actions.
👤 Privacy
The right of individuals to control the collection, storage, and dissemination of their personal information.
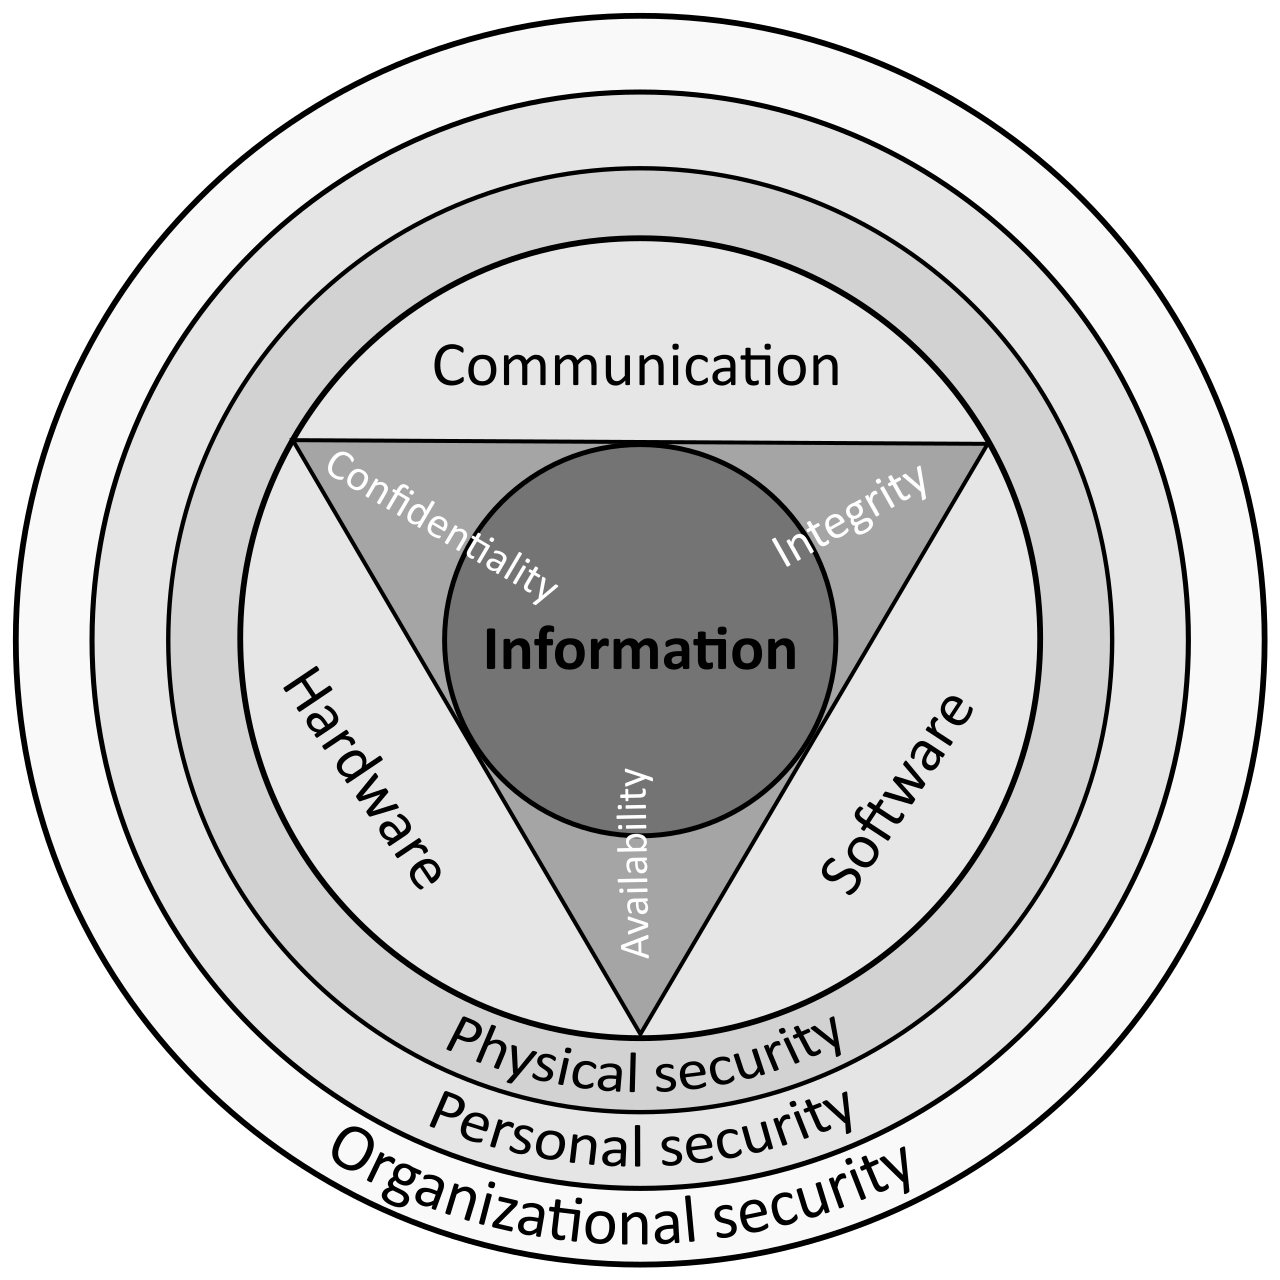
🔺 The CIA Triad: What Security Protects
🔒 Confidentiality
Only authorised people can see the data.
Exam results stay hidden until the official release.
✅ Integrity
Data is accurate and not changed without permission.
No one can secretly change a mark from 45 to 85.
⚡ Availability
Data and systems work when needed.
The results website stays up on results day.
Every security control you'll learn protects at least one of these three.
The CIA Triad
🧪 Activity: Which Part of CIA Was Broken?
1. A hacker downloads and publishes a hospital's patient records. → Confidentiality
2. A student breaks into the college system and changes their own grade. → Integrity
3. A flood of fake traffic takes a bank's website offline for six hours. → Availability
4. An employee secretly edits an invoice to send a payment to their own account. → Integrity
5. Ransomware locks every file in an office. → Availability (and confidentiality too, if the attackers also copy the files)
Why Does This Unit Matter?
Our world is increasingly digital. This reliance creates both incredible opportunities and significant risks.
- ⚡ Every transaction, communication, and piece of data is a potential target.
- 📊 Businesses, governments, and individuals are all vulnerable to digital threats.
- 🎯 The need for skilled, ethical IT professionals has never been greater.
Your Role: To build, maintain, and secure the digital infrastructure we all depend on.
Mapping the Landscape: Major Threats
We will explore several categories of threats to computer security. The most common include:
Key Threats to Investigate:
- Unauthorized Access: Gaining entry to a system without permission (e.g., hacking).
- Malware (Malicious Software): Viruses, worms, and ransomware designed to cause harm.
- Software Piracy: The illegal copying, distribution, or use of software.
Each of these will be covered in detail in upcoming chapters.
🏠 Threat, Vulnerability, Risk
⚠️ Threat
Something that could cause harm.
🏠 A burglar in the area
💻 A hacker or a piece of ransomware
🕳️ Vulnerability
A weakness a threat can use.
🏠 A window left unlocked
💻 An unpatched server or a weak password
🎲 Risk
How likely the harm is, and how bad it would be.
🏠 Unlocked window + burglar nearby = high risk
You usually can't remove threats, but you can fix vulnerabilities. That's how risk goes down.
Threat Focus: Malware vs. Piracy
🦠 Malware
Software intentionally designed to cause damage to a computer, server, or network.
- Goal: Damage, disrupt, steal.
- Examples: Viruses, Ransomware, Spyware.
- Impact: Data loss, financial theft, system failure.
💿 Software Piracy
The unauthorized copying, distribution, or use of copyrighted software.
- Goal: Avoid payment, illegal distribution.
- Examples: Using one license on many PCs, downloading "cracked" software.
- Impact: Financial loss for developers, security risks from unofficial software.
Building Our Defenses: An Intro to Controls
While threats are numerous, we have powerful tools and strategies to protect our digital assets. These are known as security controls.
🎯 The goal of a security control is to prevent, detect, or minimize the impact of a security incident.
We'll start by looking at two fundamental network security controls...
Key Controls: Firewall & Encryption
🧱 Firewalls
A network security system that monitors and controls incoming and outgoing network traffic based on predetermined security rules.
Think of it as a digital security guard at the gate of your network.
🔐 Encryption
The process of converting data into a code (ciphertext) to prevent unauthorized access. The data can only be read after it's decrypted with the correct key.
Think of it as writing a message in a secret language that only the recipient can understand.
The Bigger Picture: Law and Ethics
Technical skills are only part of the story. As an IT professional, you have legal and ethical responsibilities.
Cyber Law: Laws relating to the internet and internet-related technologies. It governs online activities and transactions, defining what is legally permissible.
Copyright: A legal right that grants the creator of an original work exclusive rights for its use and distribution. This is the foundation of anti-piracy laws.
Practical Application: The Nepali Context
These global issues have significant local impact.
Thinking Locally:
- Cyber Law in Nepal: The Electronic Transactions Act, 2063 (2008) is the primary legislation governing cyber activities. It covers unauthorized access, piracy, and online privacy.
- Local Challenges: Software piracy is widespread in Nepal, posing risks to both users (malware in cracked software) and the local software economy.
- Recent Events: High-profile data breaches of Nepali companies and government websites highlight the urgent need for better security practices and skilled professionals.
Key Takeaways
- ✅ The Digital Triad: Security, Ethics, and Privacy are interconnected and essential for modern IT.
- ✅ Threats are Real: We must understand threats like unauthorized access, malware, and piracy to combat them effectively.
- ✅ Controls are Our Tools: Firewalls and encryption are fundamental tools for protecting networks and data.
- ✅ Responsibility is Key: IT professionals must operate within legal frameworks (Cyber Law, Copyright) and strong ethical guidelines.
Unauthorized Access and Protection
🔍 The Core Problem: Unauthorized Access
Unauthorized Access: The act of gaining access to a computer system, network, or data without permission.
This is a major security threat that can lead to:
- Data Theft (personal, financial, corporate)
- Identity Fraud & Financial Loss
- System Damage or Disruption
Locked Out

🛡️ Our Defense: Access Control & Authentication
Access Control
The process of restricting who can access a resource.
It's like having a lock on your door.
Authentication
The process of verifying a user's identity.
It's the key that opens the lock.
Access control is the goal; authentication is the method.
🛂 Authentication vs Authorization
Authentication: "Who are you?"
✈️ At the airport, the officer checks your passport.
💻 You log in to the college portal with your ID and password.
Authorization: "What are you allowed to do?"
✈️ Your boarding pass lets you onto one flight and one seat, not into the cockpit.
💻 A student can view their own marks, and a teacher can edit marks.
Authentication always comes first, and authorization comes second.
🎬 Factors and MFA
📊 The Three Factors of Authentication
Authentication relies on verifying one or more "factors" to prove your identity.
1. Something You Know
Information only you should know.
Examples:
- Password
- PIN
2. Something You Have
A physical object in your possession.
Examples:
- ATM Card
- Security Token
3. Something You Are
A unique physical trait (biometrics).
Examples:
- Fingerprint
- Face ID
🧠 Factor 1: Something You Know
This is the most common factor, but often the weakest link in security.
🤔 Discussion: What makes a password "strong"?
- Length (12+ characters)
- Complexity (upper, lower, numbers, symbols)
- Uniqueness (not reused across sites)
🧮 Worked Example: How Long to Crack It?
Illustrative: a powerful cracking rig tries 100 billion guesses per second against a stolen password file.
8 lowercase letters
26 choices per position
268 ≈ 209 billion combinations
⏱️ About 2 seconds
12 characters, any keyboard symbol
94 choices per position
9412 ≈ 4.8 × 10²³ combinations
⏱️ About 150,000 years
Each extra character multiplies the work. A long passphrase like momo-rain-bus-tea-42 is both strong and easy to remember.
📱 Factor 2: Something You Have
This factor requires you to possess a physical item to prove your identity.
Physical Tokens
- ATM / Smart Cards
- Hardware Security Keys (e.g., YubiKey)
- Company ID Badges
Digital/Virtual Tokens
- One-Time Passwords (OTP) sent to your phone
- Authenticator App codes (Google Authenticator, Authy)
🧬 Factor 3: Something You Are
Biometrics: Authentication using unique physical or behavioral characteristics.
Common Examples
- Fingerprint Scans
- Facial Recognition (Face ID)
- Iris or Retina Scans
- Voice Recognition
Privacy Concerns?
What are the risks if your biometric data is stolen? Unlike a password, you can't change your fingerprint!
⚡ Level Up: Two-Factor Authentication (2FA)
Two-Factor Authentication (2FA): A security method that requires two different factors to verify a user's identity.
Combining factors creates a layered, much stronger defense.
Example: Password (Know) + Code from Phone (Have) = Strong Security
Even if a hacker steals your password, they can't log in without your phone!
🌍 Real Case: One Password, One Pipeline (2021)
- May 2021: attackers got into Colonial Pipeline, which carries about 45% of the fuel used on the US East Coast.
- They got in through an old VPN account using a password that had leaked online. The account had no 2FA.
- The company shut the pipeline for about 5 days, petrol stations ran dry, and it paid a ransom of about $4.4 million.
Lesson: a single second factor, such as an OTP or an authenticator code, would very likely have stopped this attack.
🎬 The Colonial Pipeline Hack
Pumps Run Dry, May 2021

🌍 Practical 2FA in Nepal
You probably use 2FA every day without realizing it!
Banking & Digital Wallets
Logging into eSewa, Khalti, or your bank's app often requires:
- Your password/MPIN (something you know)
- An OTP sent to your Ncell/NTC number (something you have)
Government & Social Media
Securing your accounts on Nagarik App, Facebook, or Gmail:
- Your password (something you know)
- A code from an authenticator app or SMS (something you have)
📝 Summary & Key Takeaways
- Unauthorized access is gaining entry without permission and is a serious threat.
- Authentication is how we verify a user's identity to prevent this.
- The three authentication factors are something you know, have, or are.
- Two-Factor Authentication (2FA) provides the strongest security by combining two different factors.
💬 Discussion Questions
- Many people in Nepal share one Netflix, Wi-Fi or even bank password with family. Which part of the CIA triad does that put at risk?
- SMS OTPs can be stolen through SIM-swap fraud. Should banks move to authenticator apps or fingerprints instead? What would that cost users?
- If your college's exam portal were hacked, who would be responsible: the hacker, the college, or a student who used a weak password?
Exam Practice 📝
Short answer
- What is the CIA triad? Explain each element with an example.
- What is unauthorized access? Give two examples.
- Differentiate between a threat and a vulnerability.
- Differentiate between authentication and authorization.
Exam Practice 📝 (continued)
Long answer
- What is computer security? Explain the major threats to an organization’s information systems and the controls used against them.
- Explain the three factors of authentication with their strengths and weaknesses.
Revise the answers in the full notes linked on the last slide.
Image & Video Credits
Images
- Cyber Airmen further defensive cyber operations skills: MSgt Renae Pittman, U.S. Air Force, public domain, via Wikimedia Commons
- CIAJMK1209-en (CIA triad): Michel Bakni, CC BY-SA 4.0, via Wikimedia Commons
- Locked Laptop Screen Cartoon: Free Clip Art, CC BY-SA 4.0, via Wikimedia Commons
- YubiKey 5C NFC: Daniel Aleksandersen, CC BY 4.0, via Wikimedia Commons
- Fingerprint scanner identification: Rachmaninoff, CC BY-SA 3.0, via Wikimedia Commons
- Out-of-service gas pumps after the Colonial Pipeline cyberattack: Famartin, CC BY-SA 4.0, via Wikimedia Commons
Videos (YouTube)
- IBM Technology, "What is Multi-Factor Authentication" (122–173 s)
- Eye on Tech, "What is the Colonial Pipeline Hack? A Timeline of Events" (52–124 s)
Thank You
Questions before we wrap this hour?
Next: Unit 9 · Session 2 — Sabotage, Crime, Piracy, and Anti-Piracy
📖 Read the full notes: Computer Security and Control · Unauthorized Access and Protection
📖 Related chapter notes
Read first, then revise with this deck: